
The Sprocket Platform:
Continuous Penetration Testing
Know What's Exploitable Today, Not Last Year
Continuous penetration testing replaces the once-a-year pentest with continuous offensive security that keeps pace with your attack surface. At Sprocket, AI agents test as your environment changes, supervised by our human, expert pentesters. Your team fixes what's actually exploitable and proves the fix held.
What Is Continuous Penetration Testing?
Continuous penetration testing, also called continuous pentesting or continuous offensive security testing, is year-round security testing that evaluates your systems as they change, rather than once or twice a year. Findings stay current, and every fix can be verified.
Why Point-in-Time Pentests Fall Behind
Annual pentests and many PTaaS offerings get outdated quickly, while your environment changes every week. Continuous penetration testing vs. traditional penetration testing isn't about testing more often. It's about testing what's true today.
Annual tests go stale on delivery
Traditional pentests take weeks to schedule and describe an attack surface that has already moved on by the time results arrive.
Slow communication stalls remediation
Waiting weeks for updates leaves your team guessing, and fixes stall when testers move on before remediation is done.
Compliance evidence expires between tests
Point-in-time reports age quickly, leaving gaps auditors notice and attackers exploit. Continuous security testing keeps your evidence current all year.
How Continuous Penetration Testing Works at Sprocket
Sprocket follows your attack surface from discovery to proof, so nothing falls between assessments.
1. Discover and test continuously
Sprocket maps your exposed assets with attack surface management, then tests them year-round across networks, applications, and attack scenarios.
Outcome: coverage that keeps pace with change.
2. Validate what's exploitable
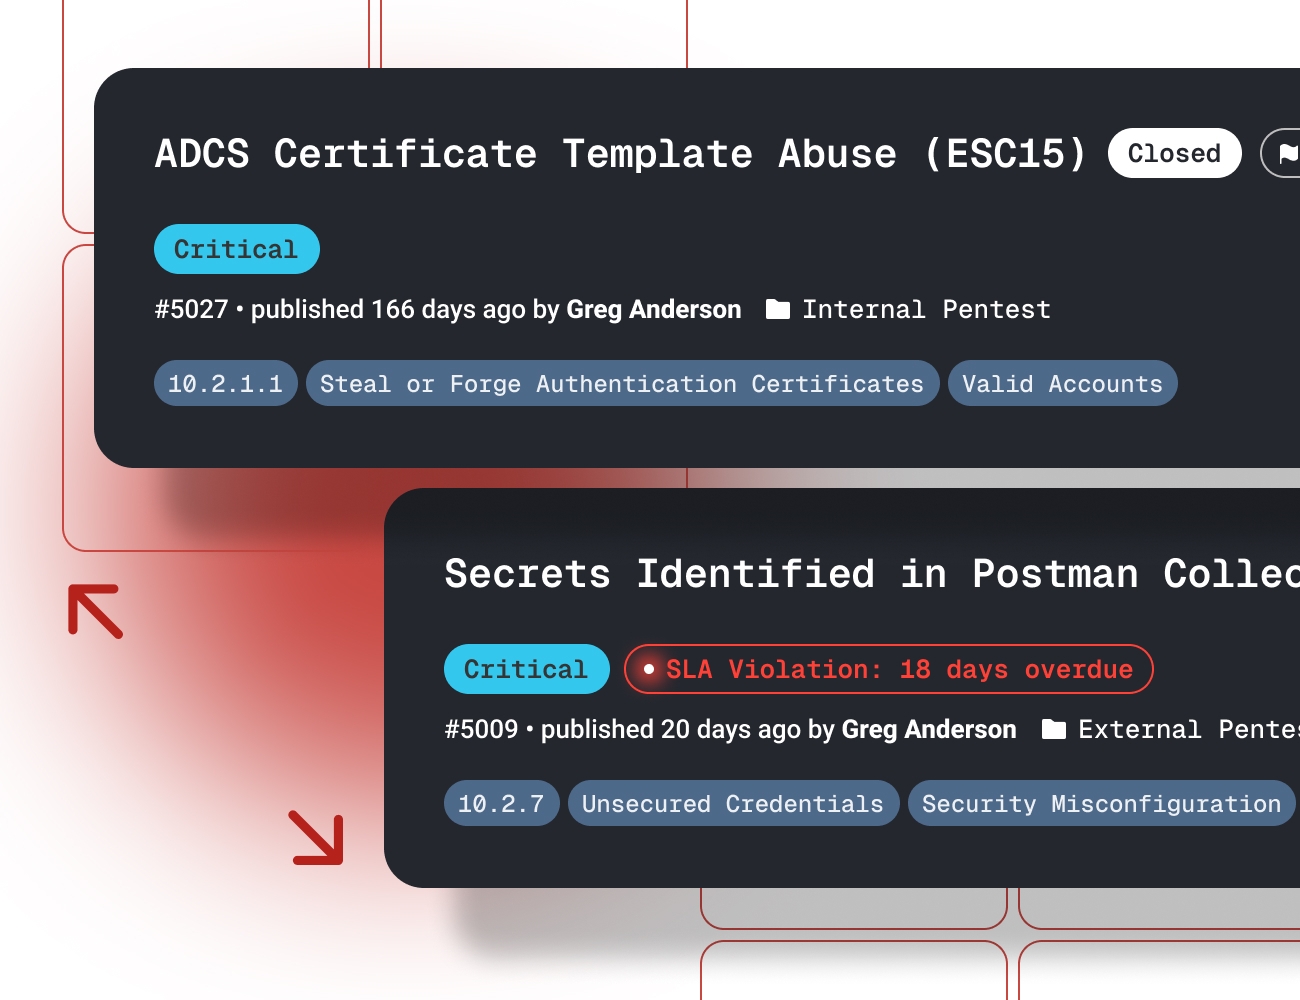
Findings are evaluated for exploitability before being published, with a step-by-step attack narrative showing how an attacker would use it.
Outcome: priorities your team can act on.
3. Fix, retest, and prove it
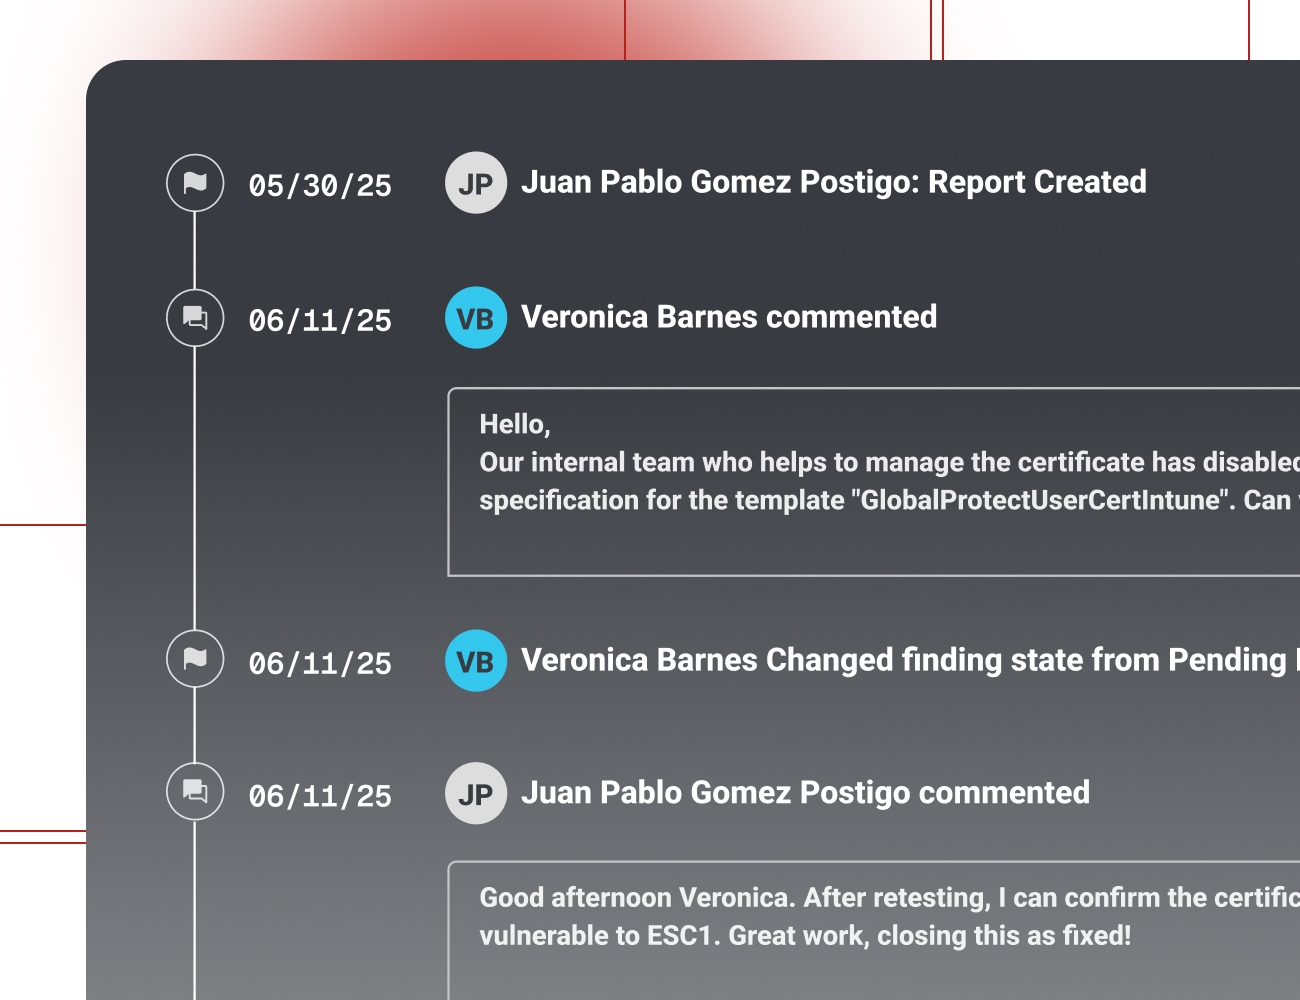
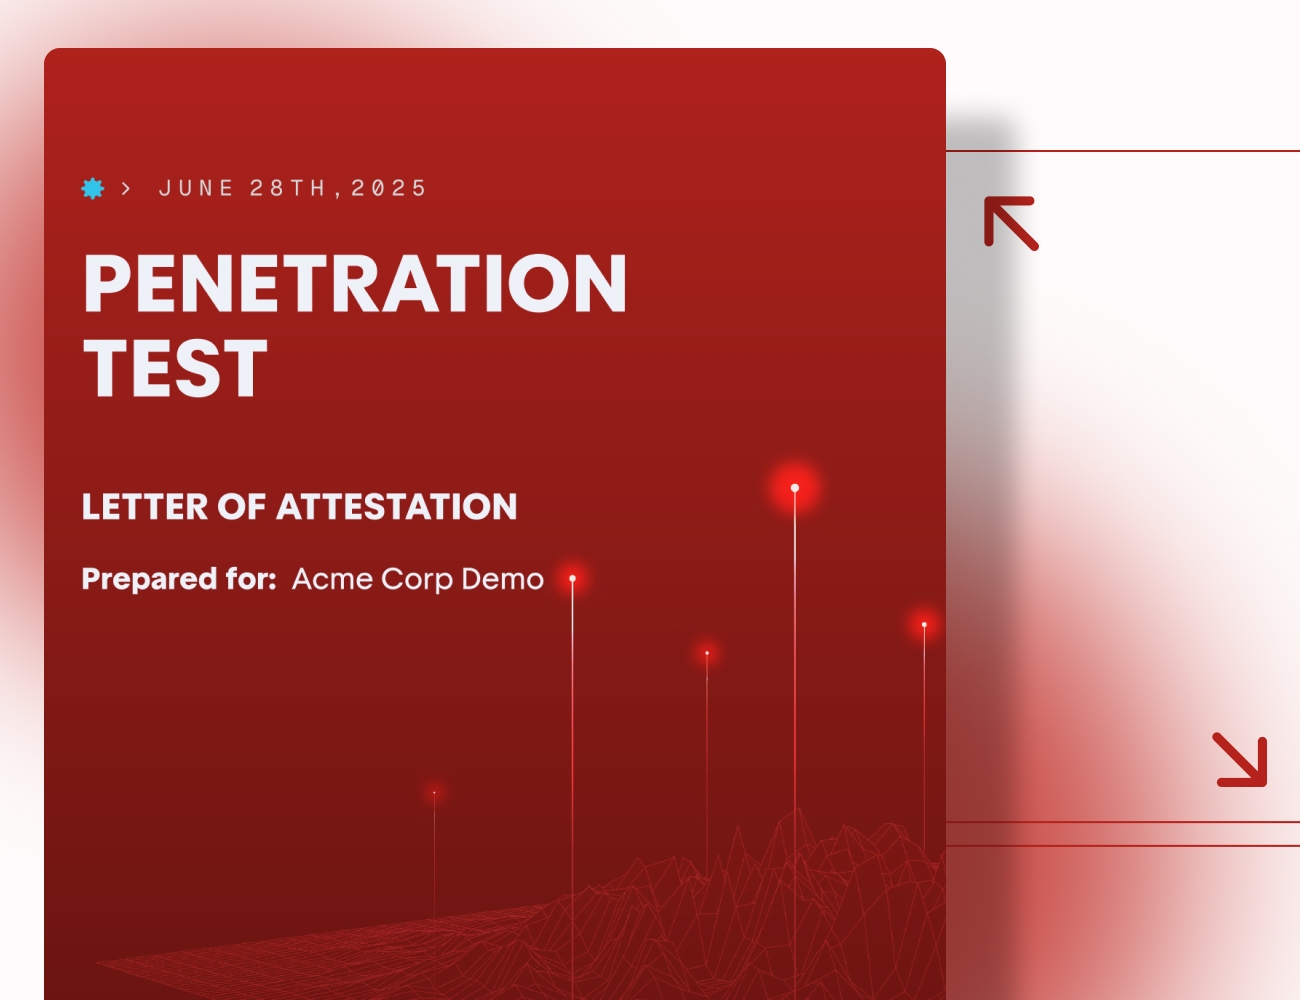
Track remediation in real time, retest as often as you need, and generate executive, compliance, and attestation reports on demand.
Outcome: proof the fix held.
AI Agents & Expert Pentesters, Working Together
Agents for coverage, experts for judgment, validation for trust.
Where AI agents lead
Sprocket's AI agents, Apex and Link, run reconnaissance, discovery, and exploitation across your web applications and APIs, then hand off to expert testers to verify impact.
Outcome: continuous coverage at speed.
Where our pentesters lead
Expert pentesters supervise the agents and take on the complex, judgment-heavy attack paths automation can't handle.
Outcome: depth where it matters most.
Every finding is validated
Agent findings clear two checks before they reach you: the agent retests every suspected issue, then a Sprocket pentester validates it. Every agent operates under the published AI Agent Safety Framework.
Continuous Penetration Testing That Drives Faster Remediation
Sprocket's continuous penetration testing services adapt to your evolving attack surface, so your team gets real-time insight instead of a report that's already out of date.
What Continuous Penetration Testing Covers
Sprocket tests critical environments as part of one continuous program, with minimal blind spots between assessments.
External Penetration Testing
The foundation of your exposure-based threat validation.
We continuously test internet-facing assets, including domains, applications, APIs, and cloud services, for exploitable risks and forgotten attack paths.
Internal Penetration Testing
Uncover how attackers move once inside.
Our testers simulate insider threats and post-breach behavior by moving laterally, escalating privileges, and targeting critical internal systems.
Social Engineering
Test the human layer of your security program.
Controlled phishing, vishing, and social engineering campaigns measure how employees respond, so you can validate awareness training.
Web Application Testing
Continuously validate application-layer security.
Our experts test modern web applications against real-world attack techniques to find vulnerabilities before they become breaches.
What You Get
- Validated findings: each comes with a step-by-step attack narrative and clear remediation guidance.
- Unlimited retesting: confirm every fix as often as you need.
- Executive summaries: a clear picture of risk for leadership and the board.
- Compliance and attestation reports: generated on demand for auditors and third parties.
- Expert guidance: direct access to the Sprocket pentesters testing your environment.
Fits Into the Workflow Your Team Already Uses
Send validated findings straight to the tools your team already works in, including Jira and Slack, so remediation moves without spreadsheets or status meetings.
What Our
Customers Say.



Real Results From Real Security Teams

See the Sprocket Platform in Action
See the Sprocket Platform in action with a short demo that connects discovery, testing, reporting, and compliance in one dashboard. Watch how exposures are validated, guidance delivered, and compliance evidence generated — showing exactly how Sprocket keeps you ahead of attackers.
In this Demo You'll See:
Frequently Asked Questions About Continuous Penetration Testing
What is continuous penetration testing?
Continuous penetration testing is year-round offensive security testing that adapts as your attack surface changes, so findings reflect what's exploitable today. See how we test.
How is continuous penetration testing different from traditional penetration testing?
A traditional pentest is a snapshot that ages on delivery. Continuous testing runs year-round, so new assets get tested and fixes get verified. Compare the two approaches.
Is continuous penetration testing a PTaaS alternative?
Yes, many PTaaS offerings deliver scheduled tests through a portal, while continuous penetration testing keeps testing as your environment changes. Read why PTaaS isn't continuous.
Does Sprocket use AI or human pentesters?
Both. AI agents test web applications and APIs at machine speed, while Sprocket's expert pentesters supervise them, test every other environment, and handle complex attack paths. Meet Sprocket's AI agents.
Is it safe to run AI agents against production systems?
Sprocket's AI agents operate under a published safety standard, and expert pentesters supervise their work. Read the AI Agent Safety Framework for details.
Do continuous penetration testing services help with compliance?
Yes. Sprocket generates on-demand executive, compliance, and attestation reports, so you can show auditors current evidence between annual tests. See how continuous testing keeps you audit-ready.
What does unlimited retesting mean?
After you fix a finding, Sprocket retests it as many times as needed to confirm the fix works and stays in place. See what's included on our pricing page.
Does Sprocket integrate with the tools we already use?
Yes. Validated findings flow into the tools your team already uses, including Jira and Slack, so remediation fits your existing workflow. See all integrations.
How much does continuous penetration testing cost?
Pricing depends on the scope of your environment and the testing you need. See how Sprocket pricing works, or request a quote for a scoped estimate.
Keep Learning About Continuous Testing
Continuous Penetration Testing: Key Benefits and How It Differs from Traditional Methods
Article
Read the articleIdentify & Exploit N-Day Vulnerabilities at Scale With Continuous Penetration Testing
Testing Lab
Read the testing labReady to Stop Testing Once a Year?
Start with a scoped assessment to see what's exploitable today, or build a continuous penetration testing program that tests as your environment changes. Either way, every finding is validated before it reaches you.
